 brivellis
Cybersecurity Awareness Programme Kit
Free · 11 files · v1.0 · Reviewed 12 Oct 2026
- 11 editable Word and Excel files
- The five pieces of evidence an auditor asks for
- Aligned with ISO/IEC 27001:2022 and NIST CSF 2.0
- Example data from Falcon Ridge IT Services in the workbooks
No sign-up. Free to use within one organisation.
What's included
| File | Component | What you use it for |
|---|---|---|
| 00 | Read Me First | The order of work, the five pieces of evidence and the standards you need |
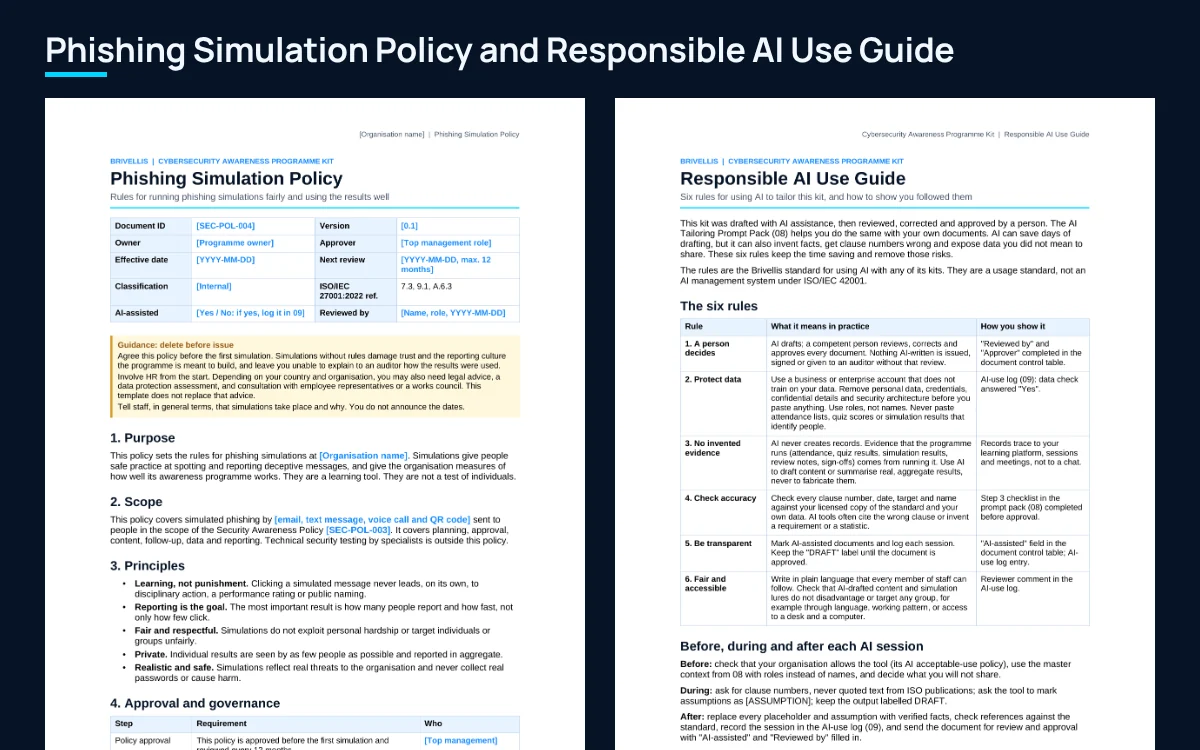
| 00a | Responsible AI Use Guide | Six rules for using AI to tailor the kit, and how to show you followed them |
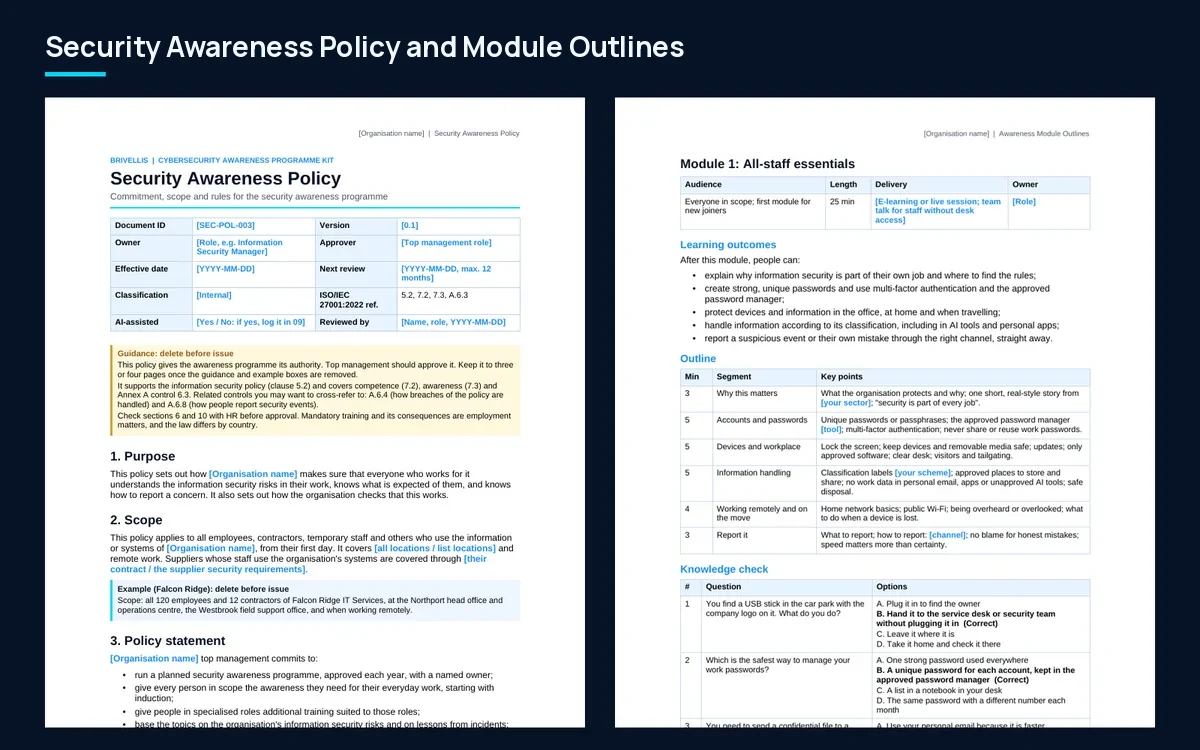
| 01 | Security Awareness Policy | Commitment, scope, roles, mandatory completion, records and privacy |
| 02 | 12-Month Awareness Programme Plan (workbook) | Audiences and a month-by-month plan linked to your risks, with approval |
| 03 | Awareness Module Outlines | Four modules, each with outcomes, a timed outline and a 5-question check |
| 04 | Phishing Simulation Policy | Fair rules for simulations: approval, no punishment for clicking, data handling |
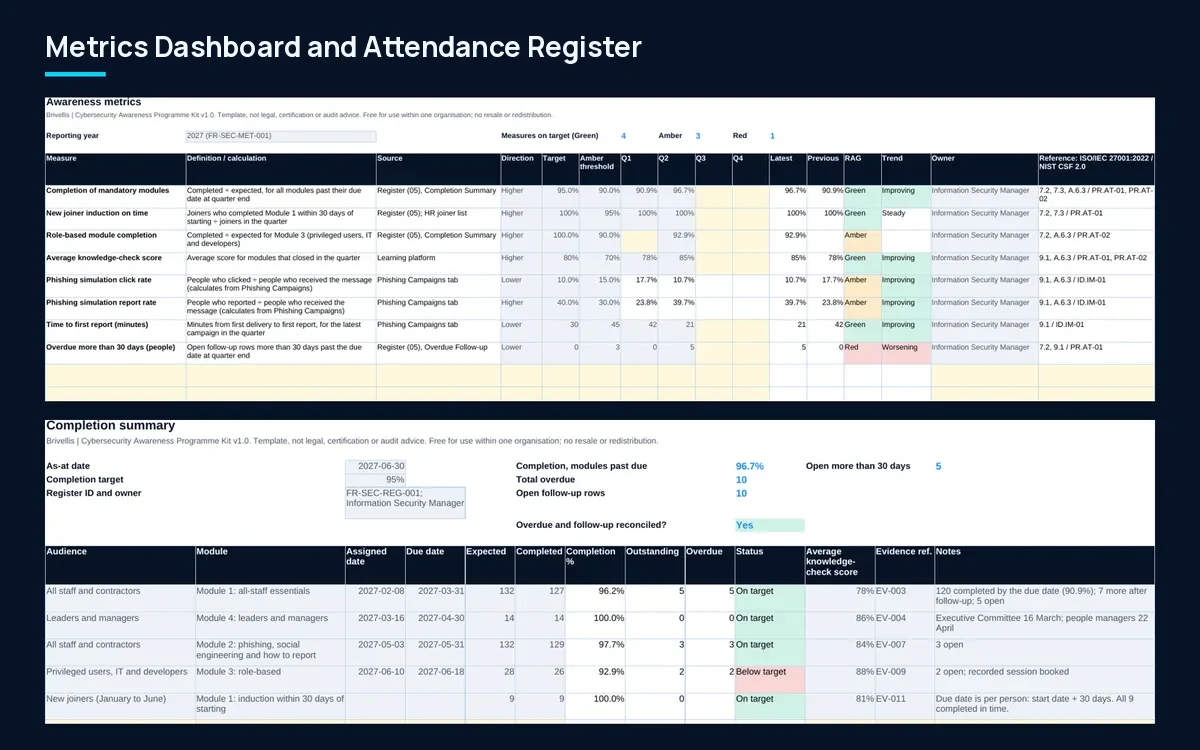
| 05 | Attendance and Evidence Register (workbook) | Expected against completed, an overdue list with follow-up, and an evidence index |
| 06 | Awareness Metrics Dashboard (workbook) | Eight measures with targets, RAG status and trend, and a review record |
| 07 | Crosswalk (workbook) | Each piece of evidence against ISO/IEC 27001:2022 and NIST CSF 2.0 |
| 08 | AI Tailoring Prompt Pack | Nine guardrailed prompts to tailor the files; every output is labelled DRAFT |
| 09 | AI-Use Log (workbook) | One line per AI session: tool, data check, reviewer, approval |
How the kit fits together
Work through the files in this order.
- PolicyFile 01
- Programme planFile 02
- Module contentFile 03
- Phishing simulationsFile 04
- Attendance and completion recordsFile 05
- Measures and reviewFile 06
Every file at a glance
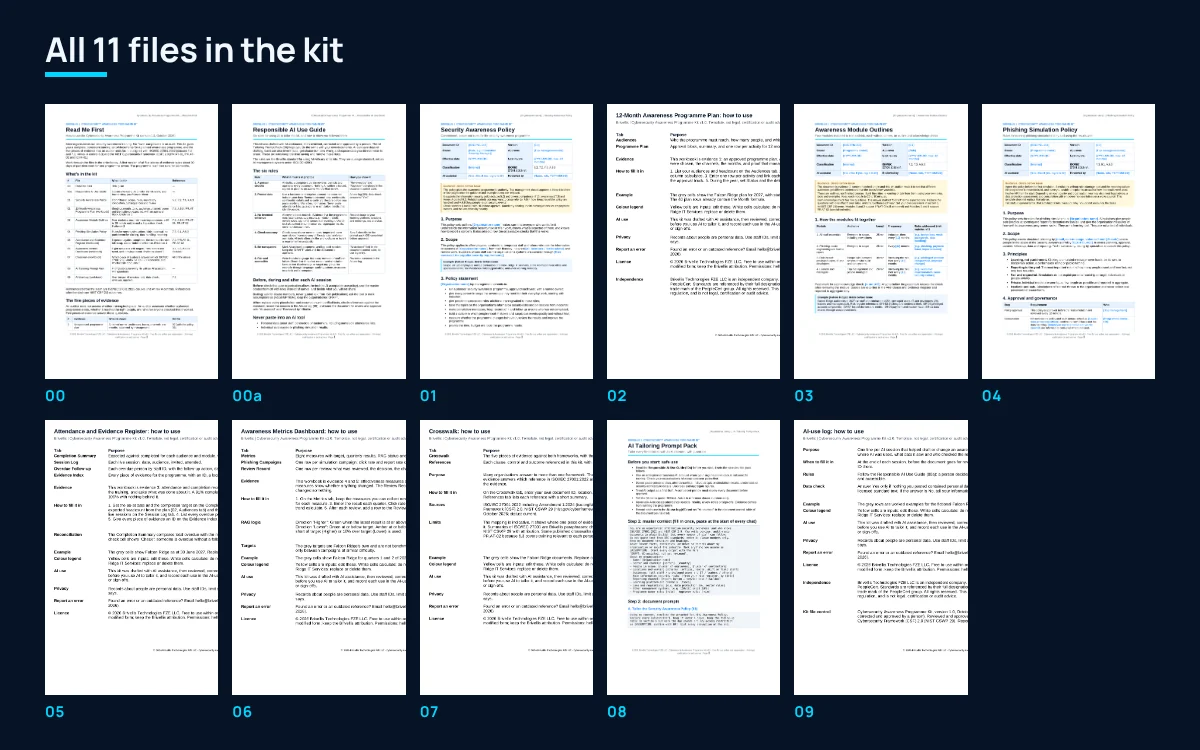
What you can use it for
Show auditors a planned programme
Produce the five pieces of evidence auditors ask for under ISO/IEC 27001:2022.
Plan a year of awareness
Set audiences and a month-by-month plan linked to your risks, then get it approved.
Run fair phishing simulations
Agree the rules first: approval, no punishment for clicking, aggregate reporting.
How we use AI
The templates were drafted with AI assistance, then reviewed, corrected and approved by a person before release. The AI Tailoring Prompt Pack helps you adapt them with your own AI tool: use a business account, keep personal and confidential data out, and have a competent person approve every document. AI never creates evidence; your records come from running the processes. Read the Responsible AI Charter.
Questions
Does this kit make us certified?
No. It is a starting document set, not certification or audit advice.
Do I need a copy of the standard?
Yes. The kit references clause numbers and does not reproduce the standard.
Is it really free?
Yes. It is free to use within one organisation, with no sign-up. You may not resell or redistribute it.
Does it include the training itself?
No. It includes outlines for four modules, with learning outcomes, key points and knowledge-check questions. You build the slides, e-learning or talks from them with your own rules and examples.
Which frameworks does it cover?
ISO/IEC 27001:2022 (clauses 7.2 and 7.3, Annex A control 6.3) and NIST CSF 2.0 (PR.AT-01, PR.AT-02, ID.IM-01). The crosswalk shows which file answers which reference.
Can I use AI to tailor it?
Yes, with care. The kit includes a prompt pack and six rules. AI drafts; a named person reviews and approves. Never use AI to create attendance records, results or sign-offs.
What changed in this version?
First release.
Start with the policy and the plan
Download the kit, read the Read Me First, then adapt the policy (01) and the 12-month plan (02).
More in this domain
Other free resources and the latest articles in Cybersecurity & Compliance.
Free kit
ISMS Starter Kit for ISO/IEC 27001:2022
13 free, editable files for an ISO/IEC 27001:2022 ISMS, from scope to management review, with a 93-control SoA and a NIST CSF 2.0 crosswalk.
Free template
Acceptable Use Policy
One editable Word policy for devices, email, cloud, remote work and AI assistants, with a signed acknowledgement form.
Free course
ISMS in Practice: Implementing ISO/IEC 27001:2022 (Free Course)
A free video course that walks through the ISMS kit, template by template.
Latest articles
- NIST CSF 2.0 explained: how to answer it from the ISO/IEC 27001 system you already run
NIST CSF 2.0 in plain terms: the six functions, what changed in version 2.0, and how an ISO/IEC 27001 ISMS answers it without a second control set.
- ISO/IEC 27090 is out: how the new AI security standard fits with ISO/IEC 42001
ISO/IEC 27090:2026 gives guidance on AI-specific security threats. Here is how it differs from ISO/IEC 42001 and how to use the two together.
- How to implement ISO/IEC 27001:2022: the seven ISMS documents to build first, in order
ISO 27001 implementation, step by step: the seven ISMS documents to build first, the order that works, and how risk, controls and evidence stay linked.
More free template kits
SMS Starter Kit for ISO/
Free · 17 files · v1.1
Scope, policy, SLA, plan and review templates with a worked example.
BCMS Starter Kit for ISO 22301
Free · 14 files · v1.0
BIA workbook, continuity plan, IT DR runbook and exercise pack.
ISMS Starter Kit for ISO/
Free · 13 files · v1.0
Scope, policy, risk register, SoA skeleton and audit plan.
© 2026 Brivellis Technologies FZE LLC. Free to use within one organisation. No resale, redistribution or republication, in original or modified form; keep the Brivellis attribution. Permissions: [email protected].
Brivellis Technologies FZE LLC is an independent company. It is not affiliated with, endorsed by, or licensed by ISO, IEC, NIST or PeopleCert. Standards are referenced by their full designation (e.g., ISO/IEC 27001:2022) and are not reproduced. ITIL® is a registered trade mark of the PeopleCert group. All rights reserved. This material paraphrases requirements, does not reproduce any standard or regulation, and is not legal, certification or audit advice.